
Common IT Failures Businesses Accept as “Normal” — Until They Become a Serious Risk

By Corey Joinville
President & Chief Information Officer, AnchorPoint CIO Inc.

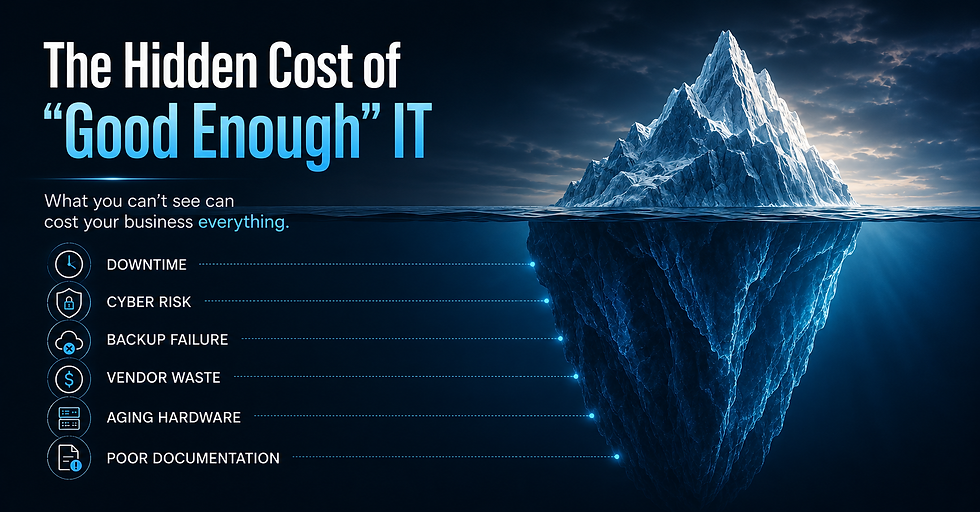
Many businesses do not have a major IT problem because of one single failure.
They have risk because small issues are accepted as normal for too long.
A slow computer here. A backup warning there. An employee using a personal device. A vendor renewing a contract without review. A server room that “works fine” until it does not.
These issues often become part of the daily routine. The business adapts around them instead of correcting them.
That is where risk builds quietly.
1. Slow Systems and Network Delays
When employees wait for files to open, applications to load, or systems to respond, it is often dismissed as “just how it is.”
But slow technology creates real business cost.
Lost time, frustrated staff, reduced productivity, and delayed work all add up. In manufacturing, engineering, agriculture, legal, medical, and professional environments, slow systems can directly affect operations and customer service.
Technology should support the business, not slow it down.
2. Backups That Are Assumed to Work
Many organizations believe they are protected because “we have backups.”
The real questions are:
Can the backups be restored? Are they protected from ransomware? Are they monitored? Is there an offsite or immutable copy? When was the last test restore completed?
A backup is not a recovery strategy until it has been validated.
3. No Clear IT Roadmap
Some businesses only replace equipment when it fails.
That creates emergency spending, downtime, and rushed decisions.
A proper IT roadmap helps leadership plan for server replacements, workstation refreshes, software renewals, cybersecurity improvements, cloud services, phone systems, and infrastructure upgrades before they become urgent.
Predictable planning is always better than reactive spending.
4. Vendor Decisions Without Oversight
Many businesses rely heavily on outside IT vendors, software providers, telecom companies, internet providers, copier companies, and cybersecurity vendors.
That is not a problem by itself.
The risk comes when no one is managing the vendors from the business side.
Without oversight, companies may overpay, renew unnecessary services, miss better options, or accept technical recommendations that are not aligned with business goals.
Vendor accountability matters.
5. Weak Cybersecurity Habits
Cybersecurity risk is not always caused by sophisticated attacks.
Often, it comes from basic gaps:
Shared passwords No multi-factor authentication Old computers Unpatched software Weak endpoint protection Poor email security No employee awareness training No clear response plan
These are common issues, but they should not be accepted as normal.
Cybersecurity needs to be managed as an ongoing business risk, not a one-time project.
6. No Executive-Level IT Reporting
Many leadership teams only hear about IT when something breaks or when a large invoice needs approval.
That leaves ownership and management without visibility into risk, budget, priorities, and performance.
IT should be reported in business terms:
What risks exist? What needs attention first? What is the cost of waiting? What projects are planned? Are vendors performing? Are backups and security controls working?
Executives need clear information to make informed decisions.
7. Server Rooms and Network Equipment That “Still Work”
Many businesses have aging switches, firewalls, servers, battery backups, cabling, and wireless equipment that have been running for years with little review.
The problem is that old infrastructure often fails without warning.
When critical equipment is unsupported, poorly documented, or not monitored, the business is exposed to avoidable downtime.
Infrastructure should be reviewed before failure forces the decision.
8. No Disaster Recovery or Business Continuity Plan
Every business hopes it will not face ransomware, hardware failure, fire, flood, internet outages, or major system disruption.
Hope is not a plan.
A proper disaster recovery and business continuity strategy defines what happens when systems go down, who is responsible, how data is restored, how long recovery should take, and what systems must come back first.
The time to build that plan is before an incident.
How AnchorPoint CIO Helps
AnchorPoint CIO Inc. helps businesses move away from reactive IT and toward structured technology leadership.
We provide fractional CIO and IT advisory services focused on:
Technology strategy Cybersecurity oversight Disaster recovery planning Vendor accountability IT budgeting and roadmaps Backup validation Lifecycle planning Executive-level reporting Risk reduction
Our role is to help ownership and leadership understand where the risks are, what needs attention, and how to make better technology decisions without needing a full-time CIO on staff.
For many small and mid-sized businesses, the issue is not that they lack IT support.
The issue is that they lack IT leadership.
That is the gap AnchorPoint CIO helps fill.
Technology should be planned, measured, secured, and aligned with the business — not accepted as a collection of problems everyone has learned to live with.
Written by Corey Joinville
President & Chief Information Officer, AnchorPoint CIO Inc.
Corey is a Fractional CIO helping manufacturing and industrial businesses take control of IT, reduce cybersecurity risk, and align technology with real business outcomes. With experience leading multi-million-dollar IT environments across North America, he works directly with ownership and executive teams to bring structure, strategy, and accountability to technology.


Comments